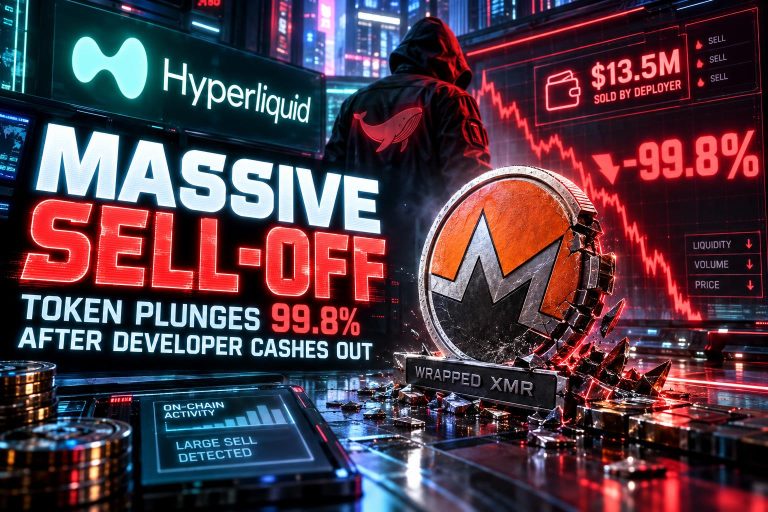




A wrapped Monero token on Hyperliquid collapsed 99.8% on Friday after an attacker drained roughly $13.5 million from the market using tokens transferred directly from the contract deployer address.
The asset, traded under the ticker XMR1, plunged from roughly $500 to $1 within 30 minutes, according to findings published by blockchain analytics firm Bitquery. The price collapse was isolated entirely to the synthetic asset on Hyperliquid and had no direct impact on Monero’s native proof-of-work blockchain or native XMR spot pricing.
On-Chain Capital Flight
On-chain records show that the primary deployer account transferred 5.2 million XMR1 tokens to a fresh wallet just before the sale. That recipient account immediately began dumping the balance across Hyperliquid liquidity pools, pulling out approximately $13.5 million.
The seller moved quickly to wash the stolen liquidity across chains. According to Bitquery’s analysis, the exploiter bridged $13.28 million in USDC over to Arbitrum. From there, $13.22 million was routed through CoW Protocol to purchase 7,467 ETH, with the vast majority of that ether immediately bridged back to the Ethereum mainnet.
Bitquery also observed that XMR1 had recently functioned as an exit route for other illicit actors. Earlier in November, attackers behind four separate exploits hitting Across Protocol, Kava, Lighter, and Safe swapped roughly $6.6 million into XMR1, apparently attempting to bridge into privacy-focused native Monero. Bitquery noted that despite this overlap in liquidity usage, no on-chain evidence links those earlier four exploits to the wallet responsible for Friday’s dump.
Hosting Breach Blamed for Key Leak
Bitquery confirmed that on-chain data cannot prove how the deployer private key was compromised or verify who had physical custody of the credentials during the transfer.
The entity behind XMR1, a bridging service called Wagyu, attributed the collapse to an external infrastructure failure. In a statement posted on X, Wagyu’s pseudonymous operator, Perpetual Cow, pointed to a security incident at hosting vendor 1984, asserting that internal customer files and server environments were compromised.
The operator claimed the private key for the XMR1 deployer had previously been stored on a server that was subsequently shut down, but alleged the hosting provider had preserved residual system files and access logs.
Perpetual Cow stated that affected traders would receive full reimbursements out of personal funds, adding that Wagyu plans to restore operations at an unspecified future date.